The Federal Court has ordered FIIG Securities to pay a $2.5 million penalty and $500,000 towards ASIC’s costs for failing to maintain adequate cyber security, and to run a compliance program overseen by an independent expert.12
What happened
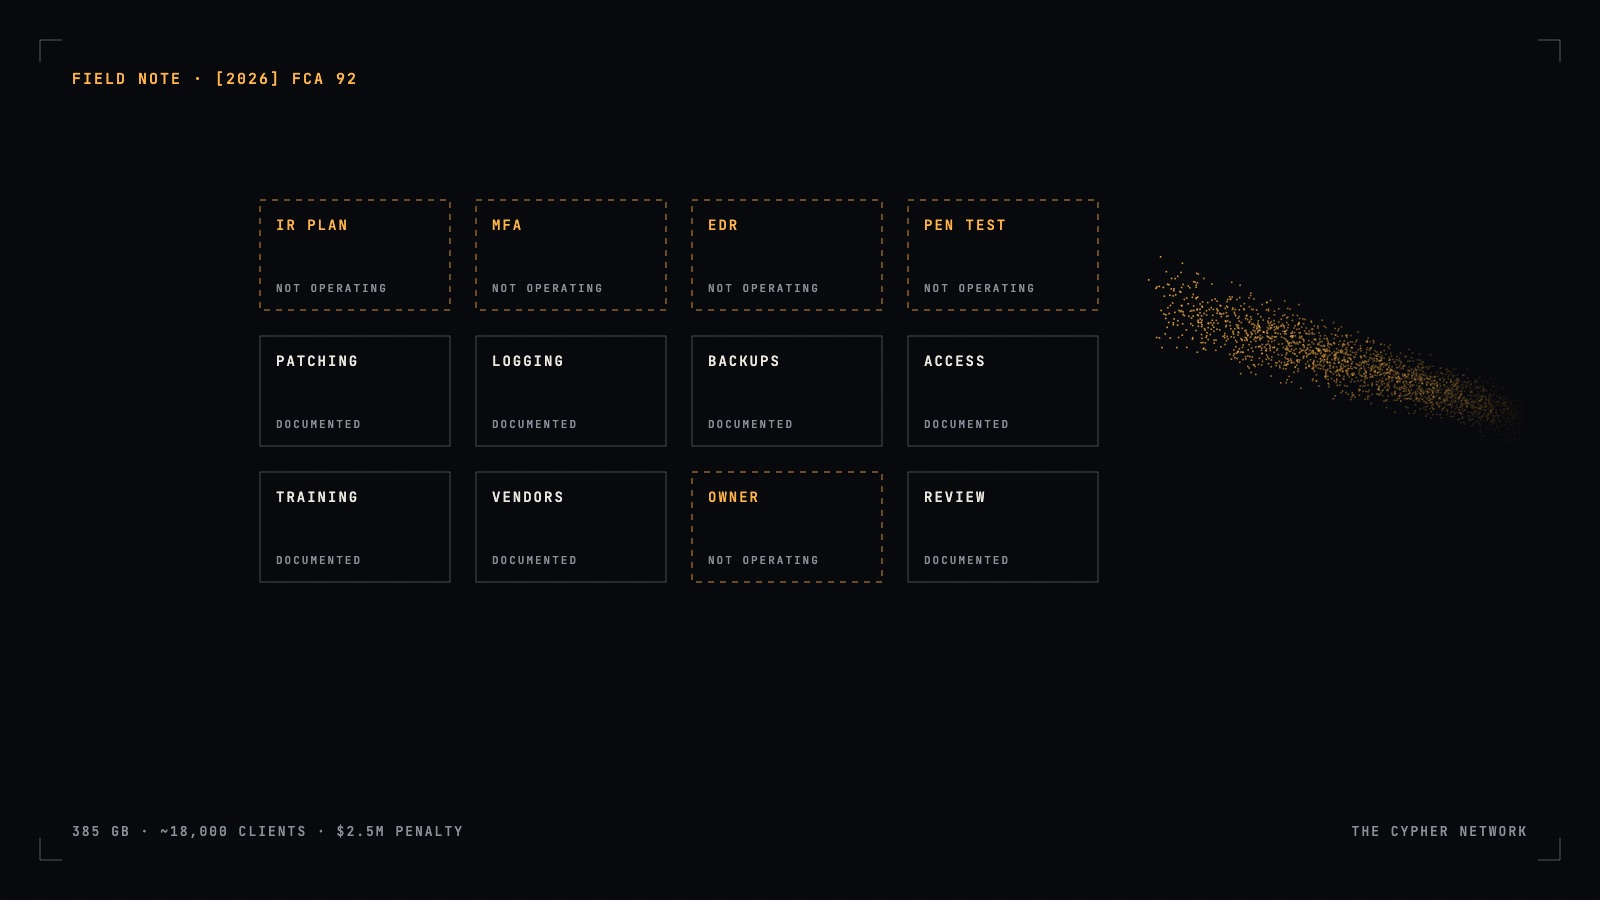
In 2023, attackers took roughly 385 gigabytes of data from FIIG, including tax file numbers and bank details, and FIIG notified around 18,000 clients that their information may have been compromised.1 FIIG learned of the breach when the Australian Cyber Security Centre alerted it on 2 June 2023.4
ASIC sued in March 2025, alleging that from March 2019 to June 2023 FIIG failed to have adequate cyber security measures in place.3 FIIG admitted it breached its AFS licence obligations, and that stronger measures would likely have let it detect the attack sooner.1
ASIC says this is the first time the Federal Court has imposed civil penalties for cyber security failures under the general AFS licensee obligations.1
Why it matters to the board
FIIG had a documented risk framework. The problem was that it was not followed, and that security leaned on people who did not have the expertise or the time for it.4 The controls at issue were not exotic: incident response planning, multi-factor authentication for remote access, endpoint detection and regular penetration testing are standard practice.4
The judgment turns “we have a policy” into the start of the conversation, not the end. Regulators will ask whether the policy was operating, who owned it, and whether that person was qualified. No action was taken against FIIG’s directors, but boards should read the case as a signal of what “adequate” now means.
Three questions for your next board meeting
- Can we evidence that our cyber controls are operating, not just documented?
- Who is accountable for cyber security, and do they have the expertise and time for it?
- Would we detect an intrusion ourselves, or would we hear about it from someone else?
How we help
A fractional CISO gives you qualified, accountable ownership without the full-time hire, and an independent view of whether your controls actually operate. See the engagement, or brief a CISO.
References
- ASIC, “26-021MR ASIC action sees FIIG Securities ordered to pay $2.5 million over cyber security failures”, February 2026. asic.gov.au
- Australian Securities and Investments Commission v FIIG Securities Limited [2026] FCA 92, judgment of 13 February 2026. asic.gov.au (PDF)
- ASIC v FIIG Securities Limited, concise statement (sealed), March 2025. asic.gov.au (PDF)
- Baker McKenzie, “Australia: Landmark penalty for cyber security failures”, February 2026. bakermckenzie.com