Field Notes
Dispatches from the boardroom and the battlefield.
FIELD NOTE 012 · 29 OCT 2026
82,000 Reports: What ASD’s 2025–26 Threat Report Means for Your Board
ASD received a cybercrime report every six minutes last financial year, and sent almost 80% more warnings to Australian organisations. Its headline finding is that AI is making attacks faster, larger and more convincing.
FIELD NOTE 011 · 03 SEP 2026
Privacy Reform, Part Two: The Draft Is Out
The Attorney-General has released an exposure draft of the second tranche of Privacy Act reforms, with submissions due 18 September. The direction is clear enough to start preparing now.
FIELD NOTE 010 · 28 APR 2026
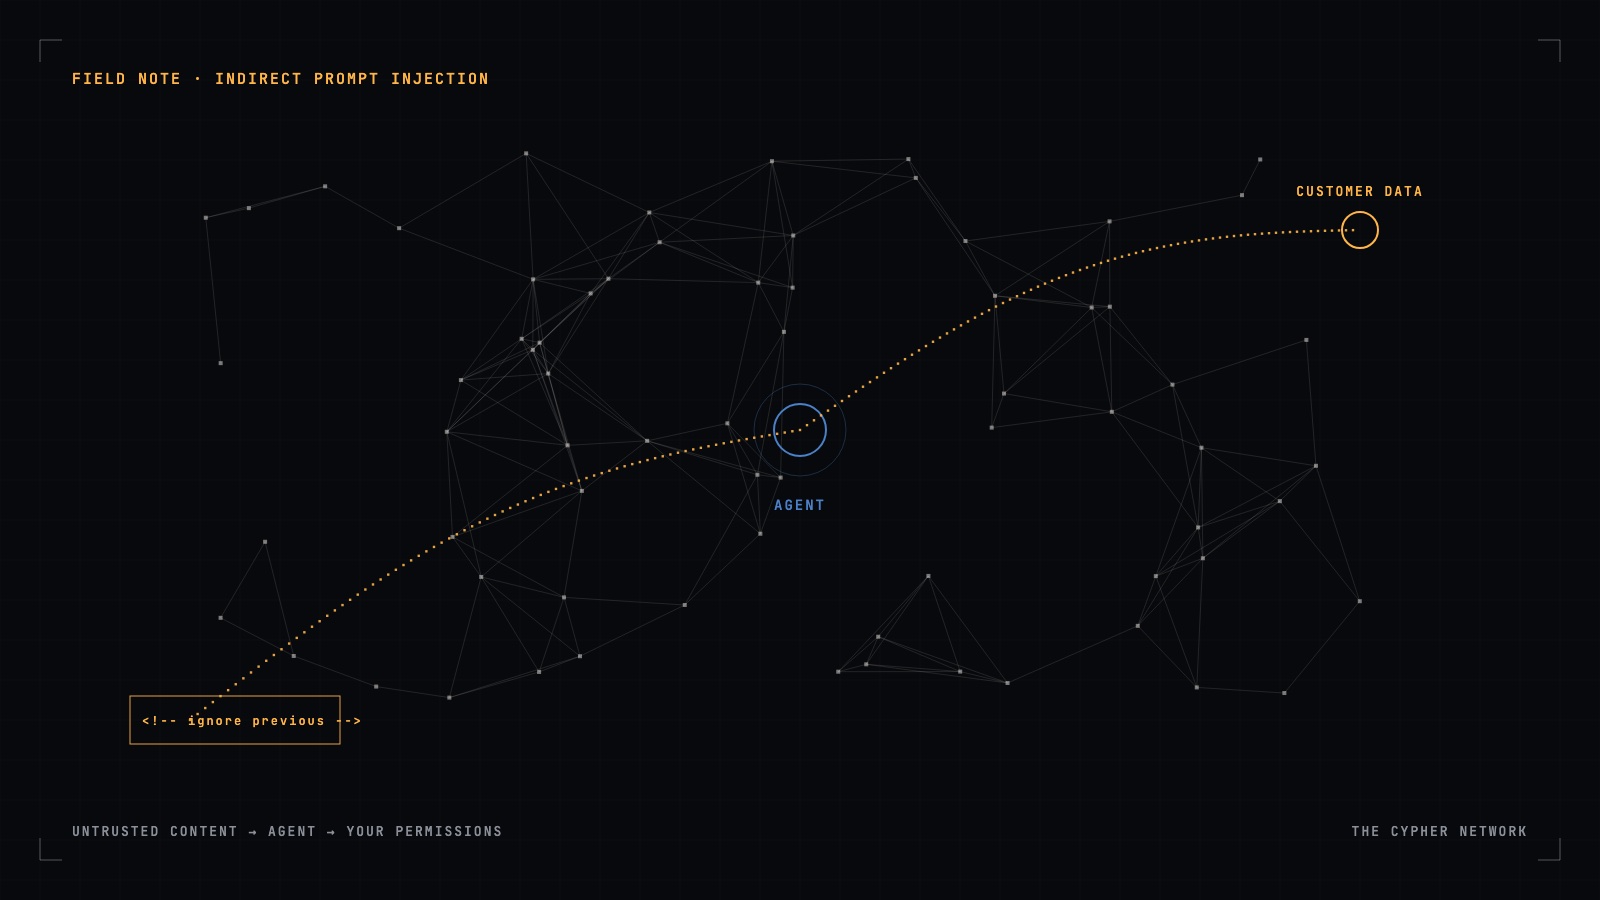
Your AI Agent Has the Keys to the Building
Indirect prompt injection has moved from research demos to attacks seen on live websites and inside production enterprise AI. If an agent can read untrusted content and act with your permissions, it can be told what to do by someone else.
FIELD NOTE 009 · 10 APR 2026
Crypto Platforms Now Need a Licence. Custody Is Where It Will Bite.
The Digital Assets Framework Act received Royal Assent on 8 April. Digital asset and tokenised custody platforms will need an AFS licence, and the security of how they hold customer assets is about to become a licensing question.
FIELD NOTE 008 · 17 FEB 2026
$2.5 Million and a Framework Nobody Followed: The FIIG Judgment
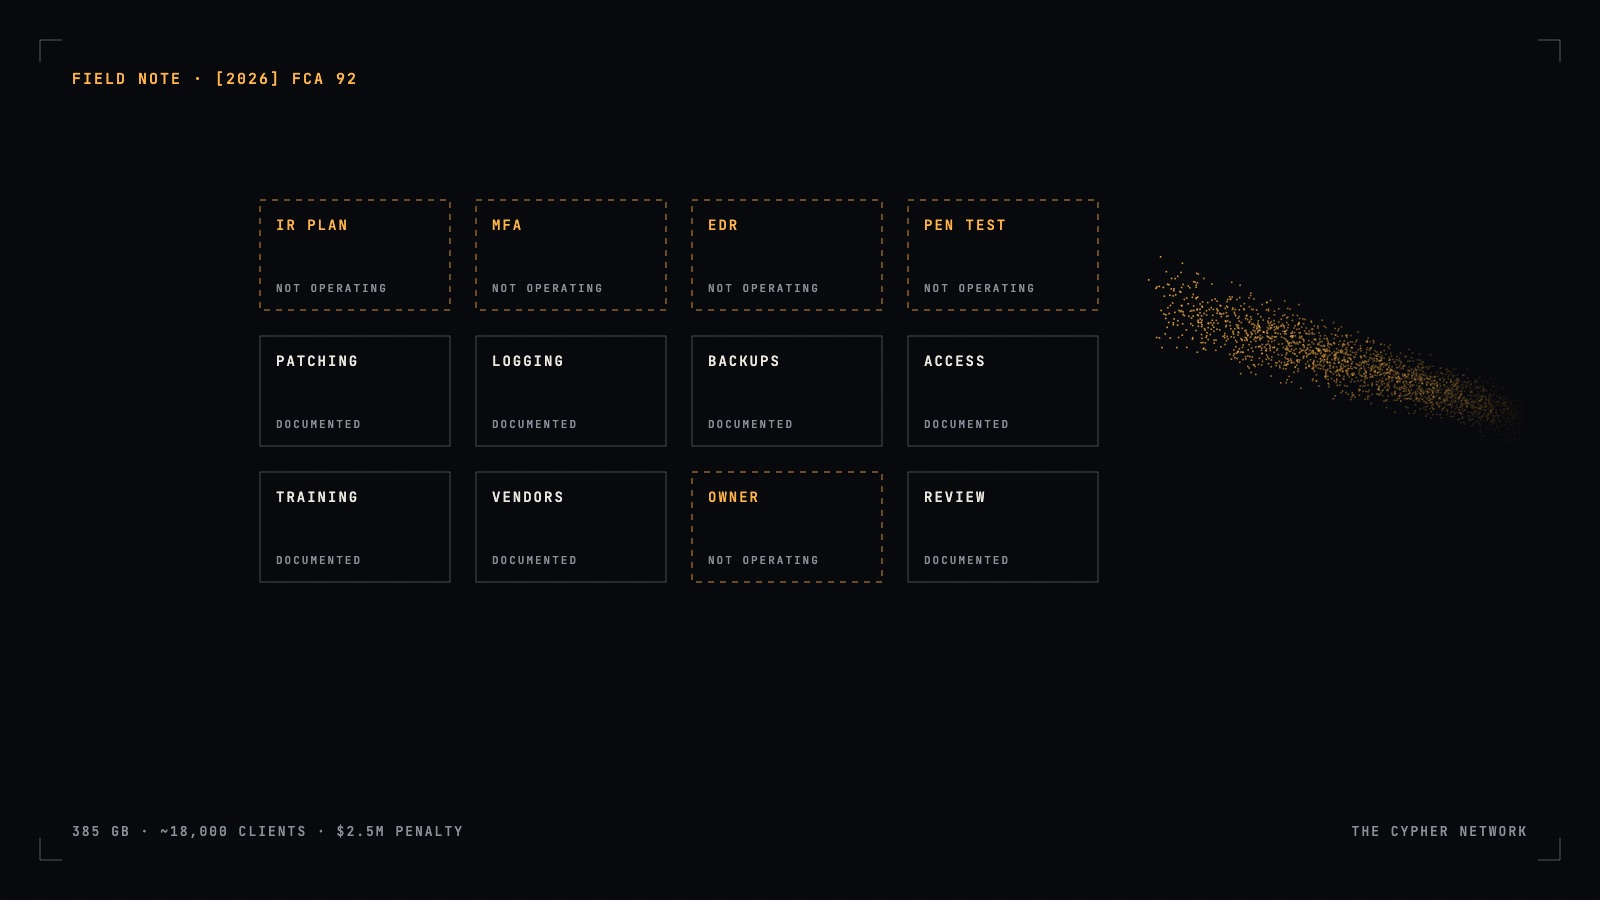
The Federal Court has ordered FIIG Securities to pay a $2.5 million penalty for cyber security failures, the first civil penalty of its kind under general AFS licence obligations. Having a policy was not a defence.
FIELD NOTE 007 · 29 SEP 2025
2030 Is Closer Than Your Encryption Refresh Cycle
ASD recommends ending the use of RSA, Diffie-Hellman and elliptic-curve cryptography by the end of 2030, with a refined transition plan by the end of 2026. For most organisations, that plan should already be under way.
FIELD NOTE 006 · 02 JUN 2025
72 Hours After You Pay: Ransomware Reporting Is Now Law
Since 30 May, Australian businesses with turnover above $3 million must report any ransomware or cyber extortion payment to ASD within 72 hours. The decision to pay is now a governance event with a clock attached.
FIELD NOTE 005 · 04 MAY 2025
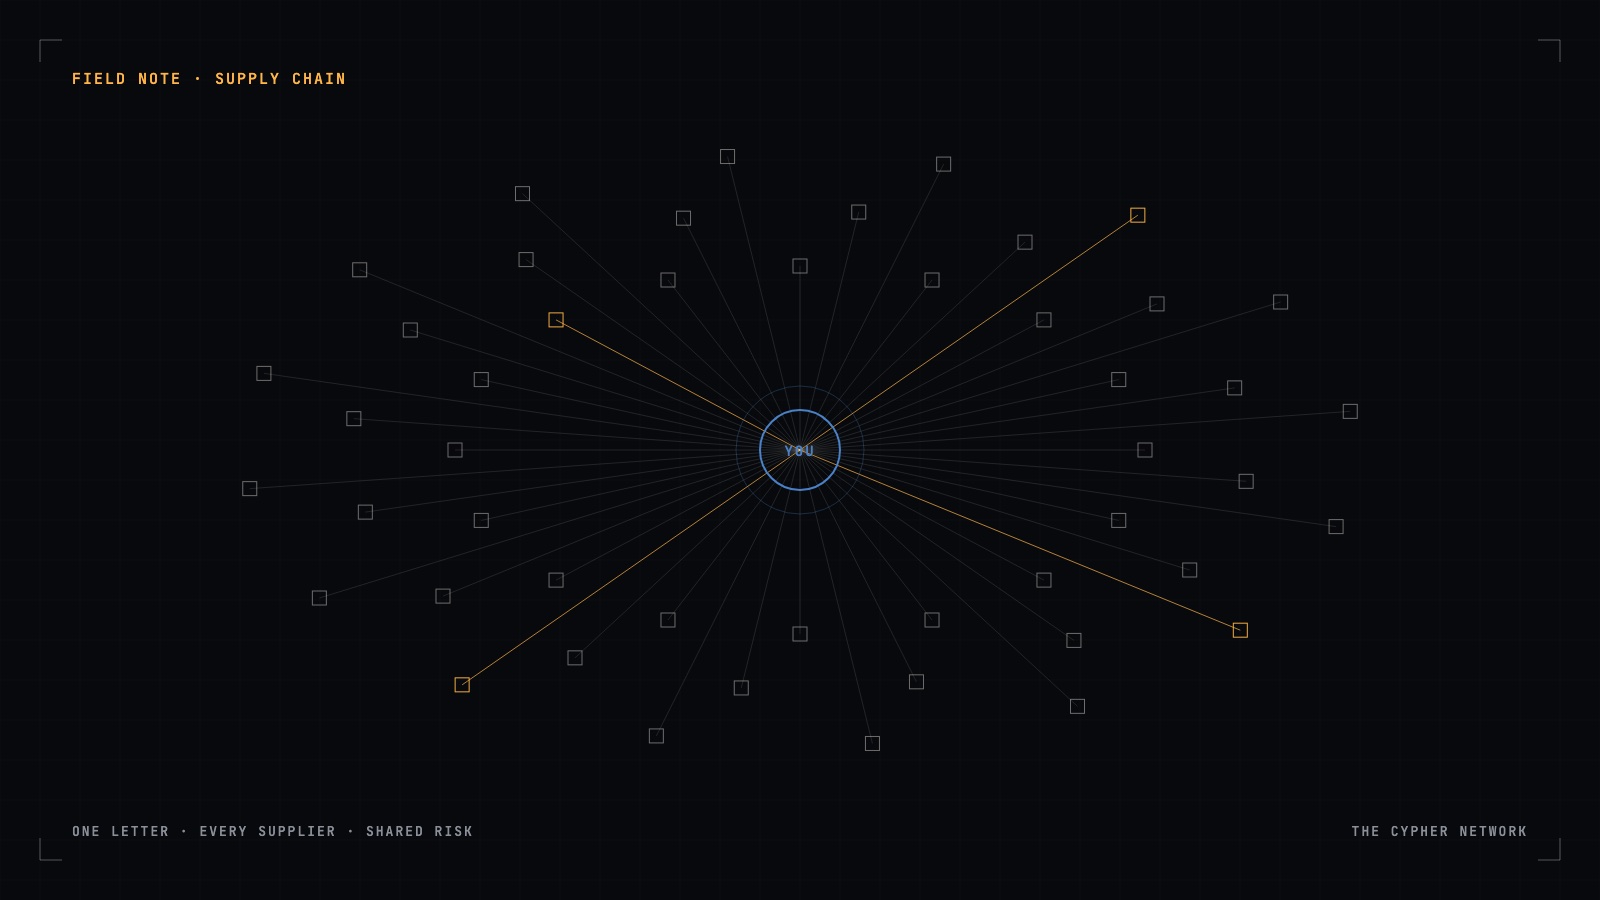
JPMorgan’s CISO letter to suppliers
We’re building AI skyscrapers on SaaS sand. And JPMorgan just handed us the blueprint for collapse. When JPMorgan’s CISO pens an open letter calling out entire supply chains for…
FIELD NOTE 004 · 03 MAY 2025
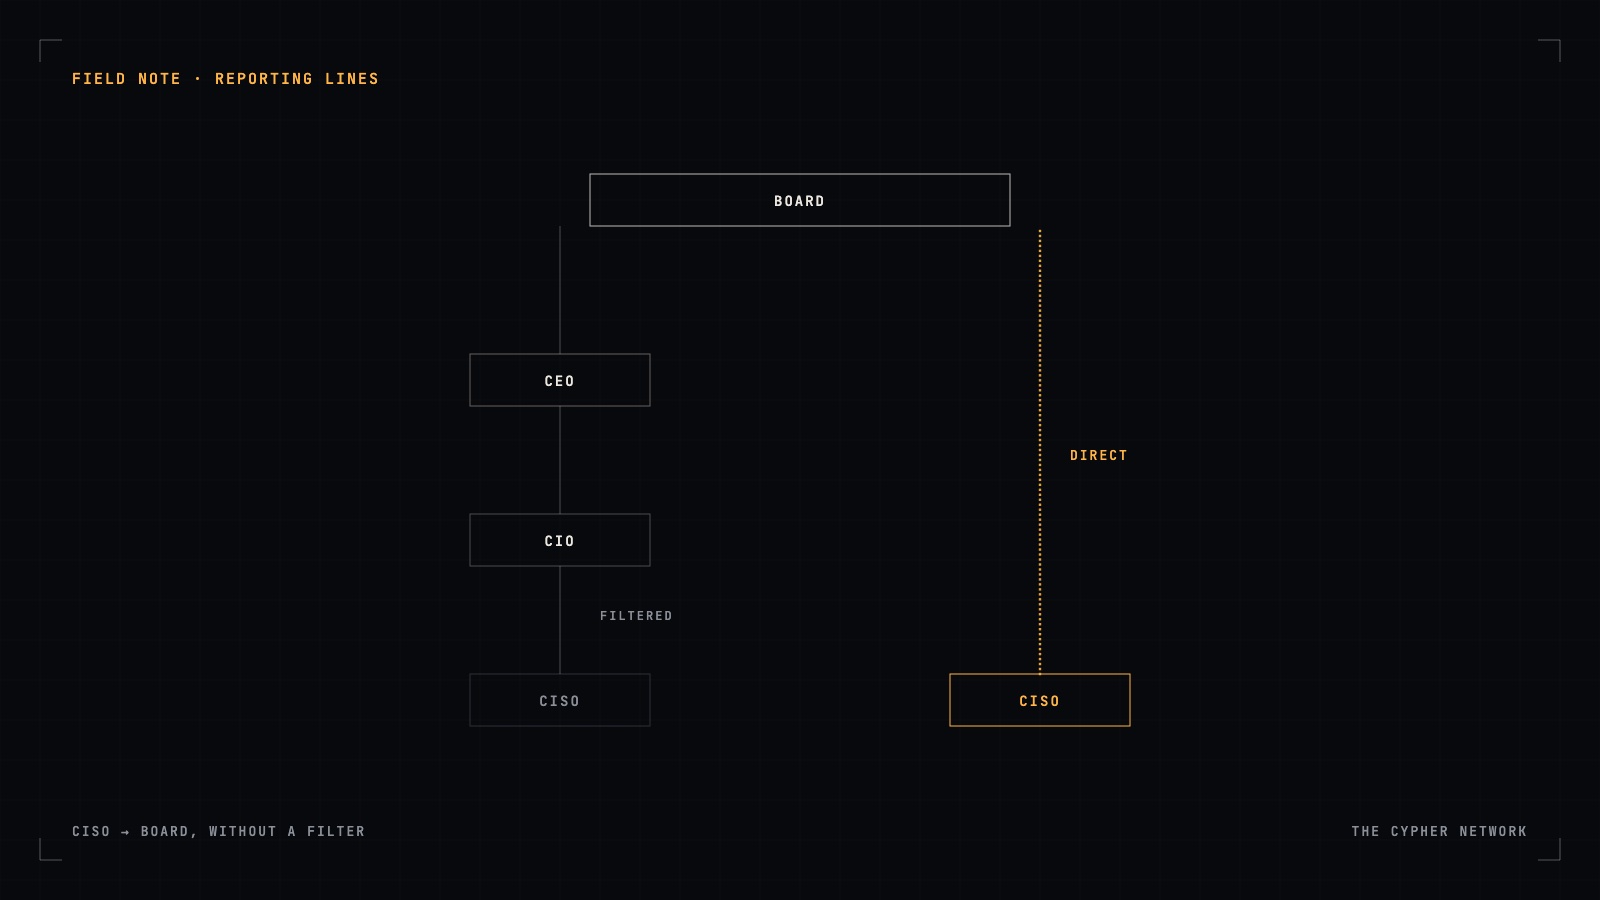
Why your CISO Should Report Directly to the Board
In today’s environment, a single cyber breach can cost millions, erode customer trust, and expose your entire organisation to regulatory action. For board executives,…
FIELD NOTE 003 · 03 MAY 2025
The Role of the CISO in the Age of AI
As a fractional CISO firm, we understand that boards and CEOs are navigating uncharted waters in the age of AI. The Chief Information Security Officer (CISO) has become…
FIELD NOTE 002 · 23 JUL 2024
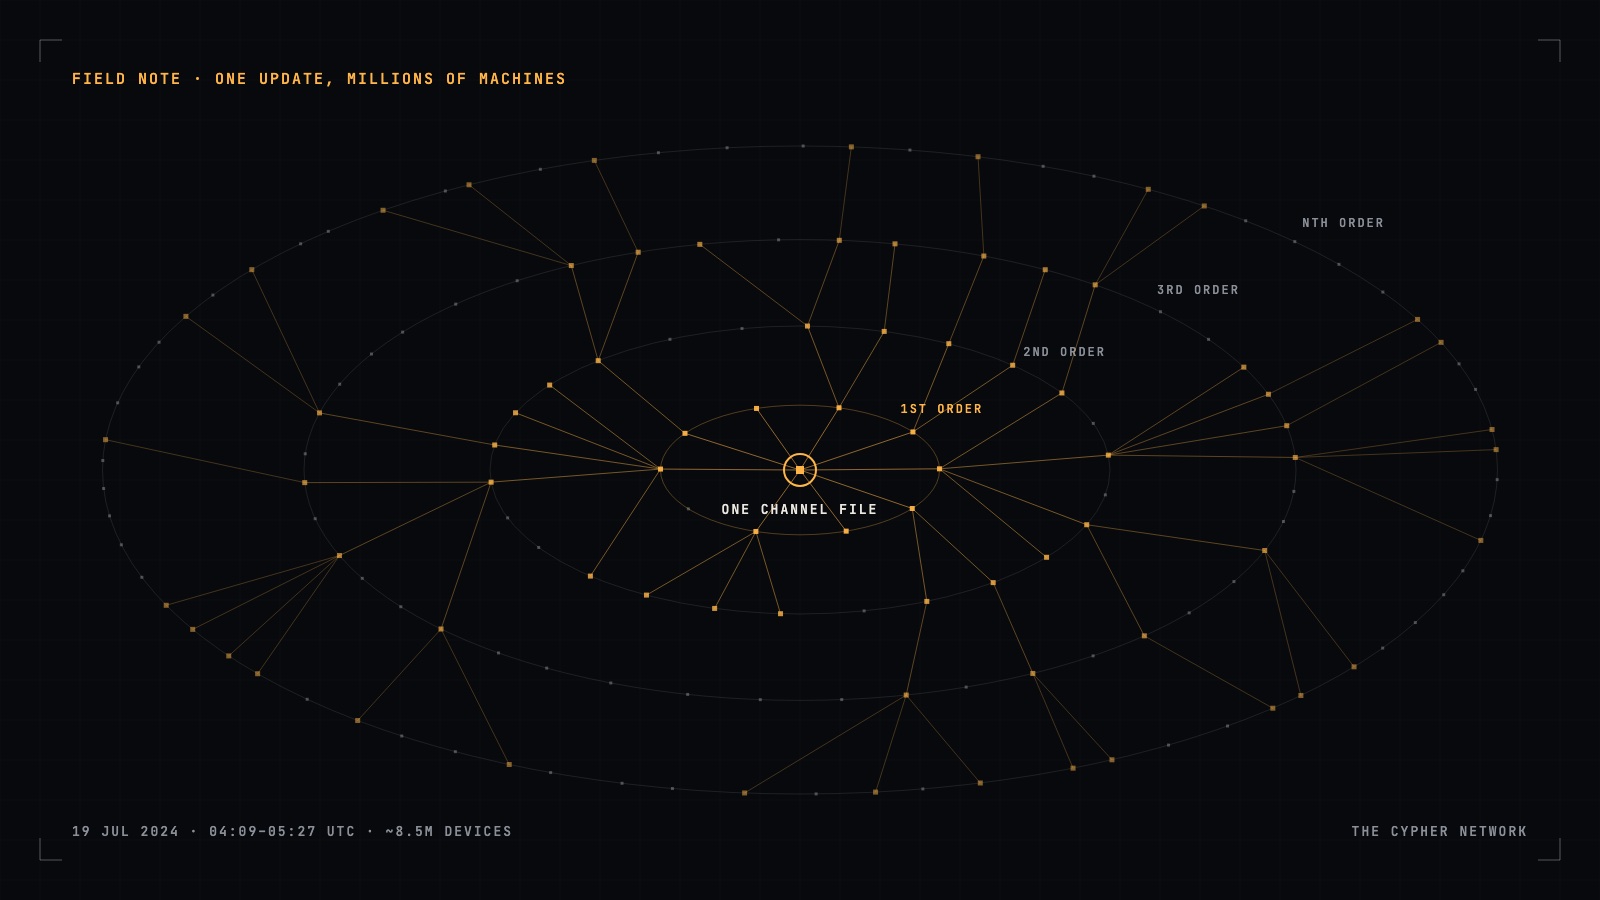
One Update, Millions of Machines: Systemic Risk Has a Face
A faulty security update crashed millions of Windows machines on Friday. It was not an attack, but it moved like one. Traced through its first, second, third and fourth-order effects, it shows why boards should ask what fails next, not just what fails.
FIELD NOTE 001 · 20 MAY 2024
The CFO on the Call Wasn’t the CFO
Arup has confirmed it lost about US$25 million after a Hong Kong employee joined a video call where every senior face was a deepfake. Your payment controls were designed for email, not for a convincing room full of colleagues.
Engage