On 30 May 2025, Part 3 of the Cyber Security Act 2024 came into force. For the first time, Australian businesses must tell the Government when they pay a ransom.12
What the law requires
- Who: any entity carrying on business in Australia with annual turnover over $3 million in the previous financial year, plus critical infrastructure entities covered by Part 2B of the Security of Critical Infrastructure Act 2018, whatever their size.23
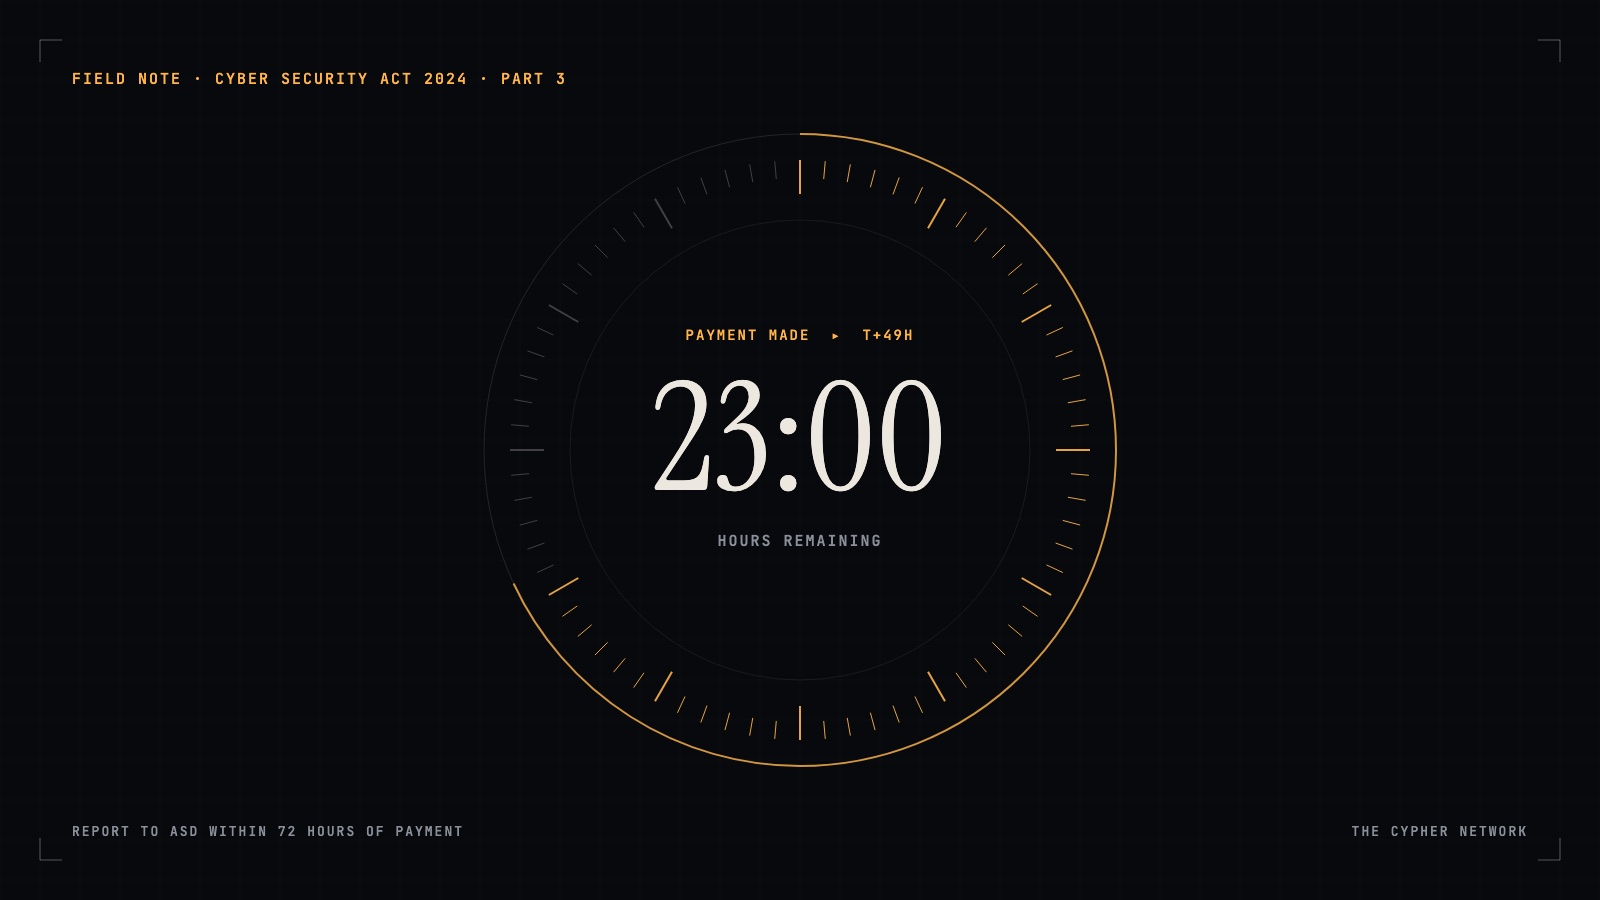
- When: within 72 hours of making a ransomware or cyber extortion payment, or of becoming aware that one was made on your behalf.1
- Where: to the Australian Signals Directorate, through the reporting form on cyber.gov.au.3
- What: details of the incident, the demand, the payment and communications with the extorting party.2
The trigger is the payment, not the demand. If you do not pay, this obligation does not apply, although other notification duties may. Failing to report exposes the business to a civil penalty.1 The Act also limits how the Government can use what you report, which is meant to encourage candour.2
Why it matters to the board
Ransom decisions used to happen in a war room, under pressure, often over a weekend. Now they come with a statutory deadline and a record that regulators will know exists. Seventy-two hours is not long when the same people are also restoring systems, briefing insurers, notifying the OAIC and talking to customers.
The board does not need to decide in advance whether it would pay. It does need to decide in advance who decides, on what information, and who owns the report.
Three questions for your next board meeting
- Is our turnover above the threshold, and does any entity in the group hold critical infrastructure assets?
- Does our incident response plan name the person who files the ASD report, and is there a 72-hour clock in it?
- Have we rehearsed a ransom decision end to end, including legal, insurer and regulator notifications?
How we help
We write the ransom decision into your incident plan, run the tabletop that tests it, and sit in the war room when it is real. See Incident & Resilience on the Practice, or brief a CISO.
References
- Cyber Security Act 2024 (Cth), Act No. 98 of 2024, Part 3. Federal Register of Legislation. legislation.gov.au
- Department of Home Affairs, “Factsheet: Mandatory ransomware and cyber extortion payment reporting”. homeaffairs.gov.au
- Australian Signals Directorate, “Ransomware payment and cyber extortion payment reporting”. cyber.gov.au
- Department of Home Affairs, “Cyber Security Act”. homeaffairs.gov.au